Cybersecurity for small business Security you can see through.

Arcline finds the gaps in your defenses, closes them, watches for trouble, and proves you could recover. Fixed prices, tools you can audit, and a written report for everything we do.

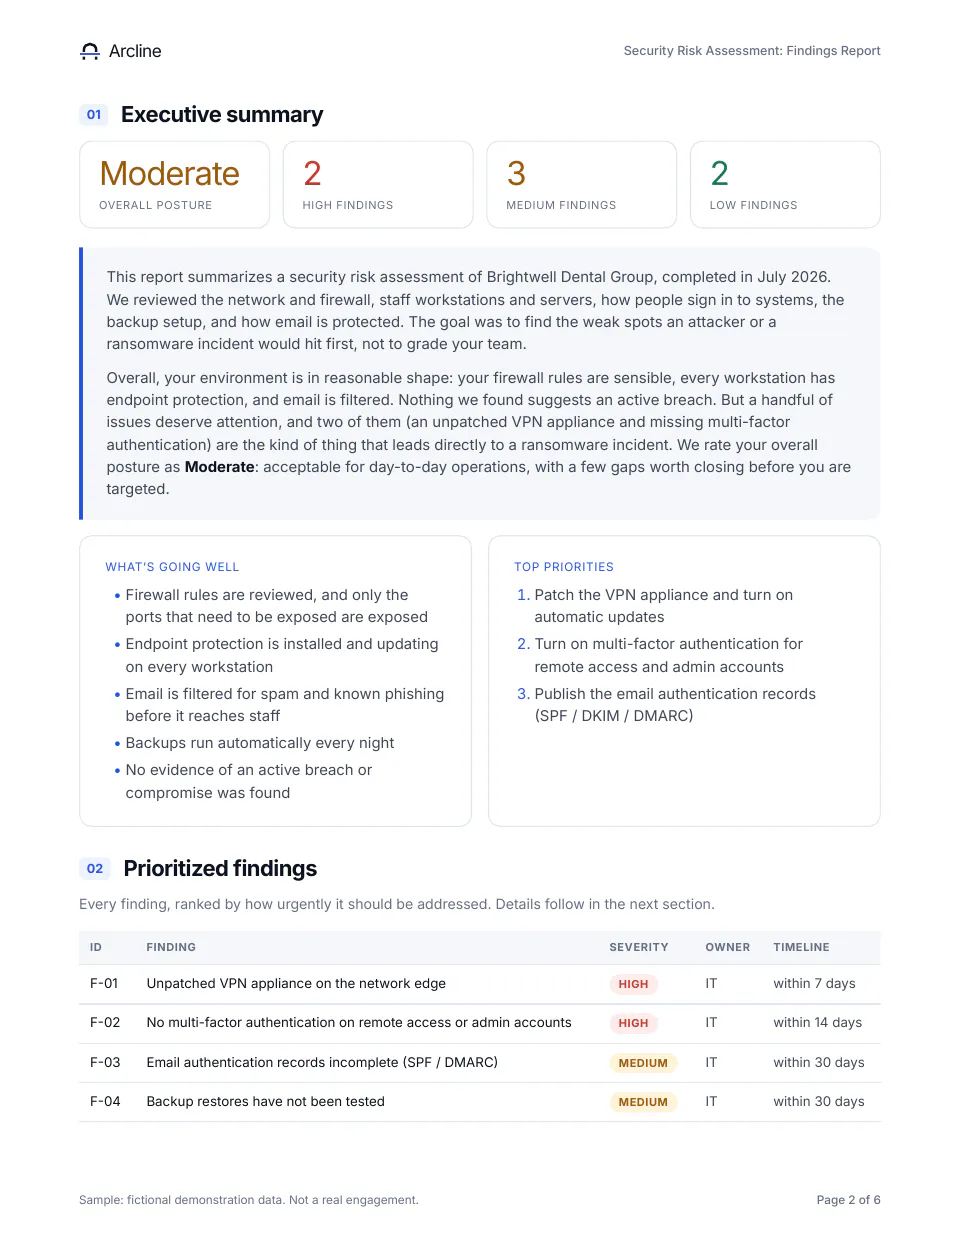
Risk assessment Sample

What to fix, in order

  1. High Remote desktop open to the internet Fix first
  2. High Backups never restore-tested This month
  3. Medium No DMARC policy on mail domain This month
  4. Low Firewall firmware one release behind Next cycle
  • $750 starting price for a fixed-price risk assessment
  • 24 hrs or less to a reply from an engineer
  • 7 security services across four stages

What we do

One job: keeping your business secure.

Four stages, in the order most clients meet us. Start anywhere, though most start with an assessment.

  1. 01

    Assess

    Know where you stand before something forces the question.

  2. 02

    Protect

    Close the gaps an attacker would find first.

  3. 03

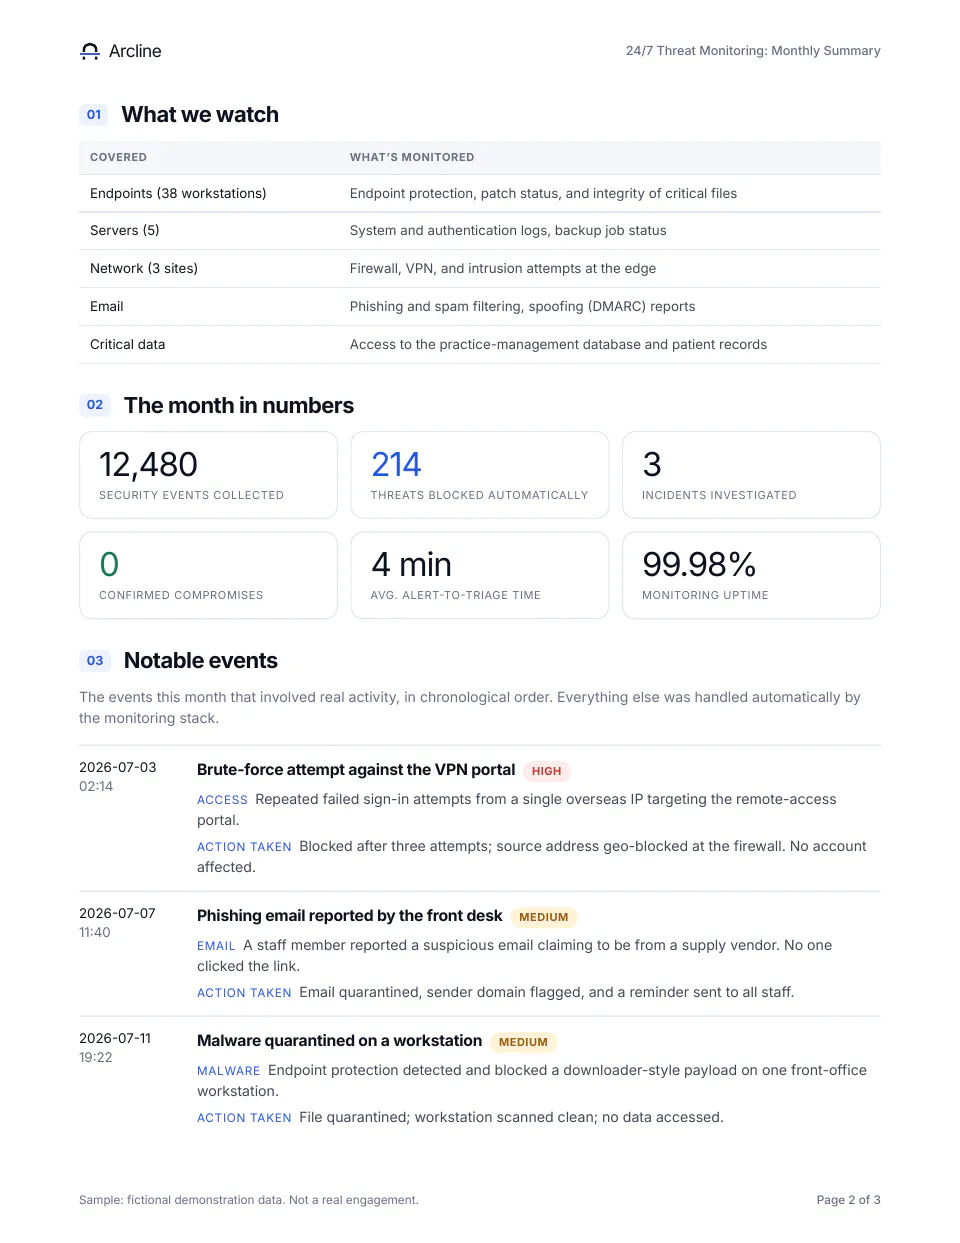
    Detect

    See trouble while it is still small.

  4. 04

    Recover

    Prove you can come back, before you need to.

The deliverable

Every engagement ends with something in writing.

Not a dashboard you have to log into. A report you can read, hand to your insurer or auditor, and act on.

  • Prioritized findings. Every issue ranked by risk and explained in plain English.
  • Auditable evidence. Raw scan exports and logs, so the work can be verified.
  • A path forward. Each finding mapped to a fix, an order of work, and what can wait.
Read the sample reports

Our commitments

What you can count on, in writing.

Auditable tooling

Your security runs on open-source tools you can inspect, such as Wazuh, WireGuard, pf, and ZFS. No black-box appliance.

Fixed price

Every project is quoted before work begins. The price you agree to is the price you pay.

One engineer

Blake scopes and delivers your project personally. Afterwards our CTO looks after ongoing support.

No lock-in

You keep the systems, the credentials, and the documentation. Stay with us because you want to.

The process

What happens when you reach out.

  1. Tell us your situation

    Plain English is fine. Describe the problem; you don't need to know the solution.

  2. We scope and price it

    You get a written scope with a fixed price: what's included, what isn't, and what you'll have at the end.

  3. We do the work

    One engineer, regular updates, and no disappearing for two weeks before a surprise invoice.

  4. You get the keys

    Every engagement ends with full written documentation. You own the result and can hand it to anyone.

Pricing

Plainly stated, quoted up front.

Security Risk Assessment

from $750 one-time

Fixed price, scoped up front

A point-in-time audit of your network, endpoints, access, and backups, ending in a written remediation report.

  • Network, endpoint, and access review
  • Vulnerability scan with evidence
  • Backup integrity check
  • Written, prioritized report
  • Plain-English walkthrough of the findings

Compliance Readiness

Custom per framework

Fixed scope and price

HIPAA, PCI DSS, or SOC 2 readiness that ends in audit-ready documentation.

  • One framework per package
  • Technical controls implemented
  • Audit-ready documentation
  • Prioritized gap list
  • Evidence prepared for your auditor

Locked down. Not locked in.

Tell us what you're dealing with. We'll work out what you need and give you a fixed-price quote. Scoping conversations are free, and we reply within 24 hours.